💛 A quick favor, if you've got a second.
We're really happy that you chose to read one of our stories and sincerely hope you'll stick around to read more. We took our paywall down — for now — but that won't last forever, and when the gate goes back up, we'd love for you to already be on the inside.
It's free. So please enter your email here and don't forget to like and follow us on all of your favorite Social Media platforms!
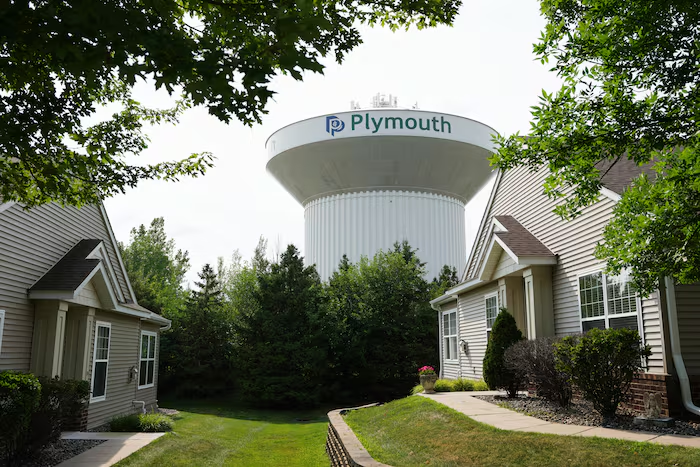
Law enforcement agencies launched an investigation Thursday into a series of coordinated cyberattacks that struck over 30 water systems across Minnesota during Sunday and Monday. Minnesota IT Services confirmed that state officials had not yet determined responsibility for the intrusions, though the FBI and other federal agencies are actively pursuing leads. No evidence of widespread public impact has emerged, though at least one municipality instructed residents to reduce water consumption briefly while response teams assessed the damage.
The FBI, working alongside the Cybersecurity and Infrastructure Security Agency and partner organizations, has refrained from publicly naming suspects. A week prior to the Minnesota incidents, these agencies issued an alert detailing sustained targeting of water and wastewater infrastructure by Iranian-linked hacking groups. The nature of the attacks—focusing on remote monitoring and control systems—aligned with the operational tactics outlined in that warning.
Cynthia Kaiser, former deputy assistant director of the FBI’s cyber division and now senior vice president of Halcyon’s Ransomware Research Center, noted Iran possesses both the motive and demonstrated capability to conduct such operations. “When it walks like a duck and talks like a duck, it’s really important to call it out,” Kaiser said, emphasizing the importance of attribution even amid incomplete evidence. Iran’s history of targeting American water infrastructure dates to 2016, when the Justice Department charged Iranian operatives connected to an attack on a dam near New York City.
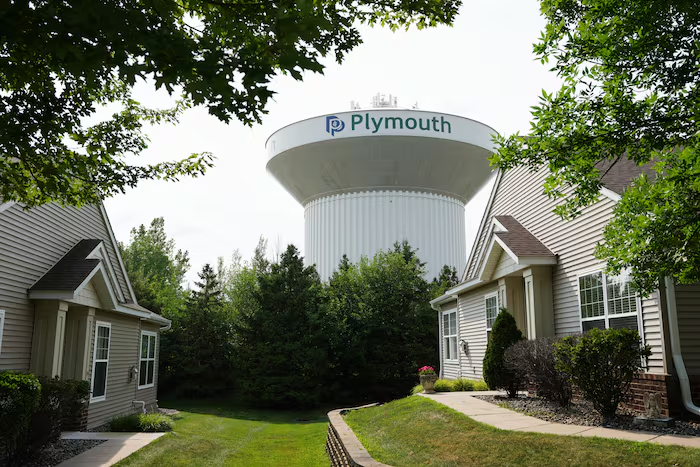
Water systems remain attractive targets for hostile actors due to weak security posture and limited resources for defensive measures at local facilities. The Braham water plant, serving approximately 1,700 residents 70 miles north of Minneapolis, went offline Monday after attackers disabled operational controls, forcing the city to rely temporarily on stored water in the tower. The city of Plymouth, with 80,000 residents outside Minneapolis, reported restored communications infrastructure by Tuesday afternoon following a similar incident, though operators maintained service continuity without disruption to water quality or supply levels.
Minnesota IT Services indicated that most confirmed compromises involved technology used to remotely manage and monitor equipment across affected systems. Investigators identified commonalities in attack timing and methodology but have not yet established whether a single actor orchestrated all incidents or multiple groups operated independently.
More Stories
Former NFL cheerleader and ex-aide face off in close Rhode Island GOP primary
Trump Threatens FCC Action Against NBC’s Welker Over Endorsement Coverage
Chicago Mayor Issues Executive Order Requiring Contractor Diversity Disclosures and ICE Ties Reporting